Hey everyone, it’s Jake from your go-to time server squad, and today we’re talking about something that’s way more critical for your business than you probably think: time servers. If you’re like most folks, you see them as just “box that keeps our clocks synced” — but let’s get real for a sec. Nothing tech-related is 100% risk-free, right? Especially when every part of your network relies on that perfect, consistent time stamp. Let’s break down the security risks, how to spot them, and yeah, how we fix ’em. Time Sever
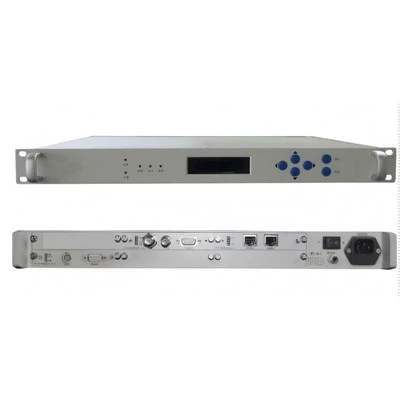
First off, let’s level set: what even is a time server? No need for the fancy textbook definition — it’s the thing that syncs all your devices (servers, firewalls, POS systems, access controls, even your work laptops) to the same, accurate time. If your time is off by even a few seconds, bad things start happening. Like, your security logs get messed up so you can’t tell when a breach happened. Your crypto transactions flip because timestamps are wrong. Your POS system overcharges customers. Yeah, not small stuff.
But here’s the catch: time servers are a target, and most of the people using ’em don’t even realize the risks until it’s too late. Let’s dive into the big ones that keep us up at night.
First up: man-in-the-middle (MITM) attacks on time sync. This is where some bad actor intercepts the signal between your device and your time server, then feeds it fake time. How do they do it? Usually by exploiting unencrypted time protocols — like plain old NTP (Network Time Protocol) without any auth. Think about that: if your server is just sending out time over the internet, anyone can listen in and swap that number. Last year, we heard from a retail client in Texas who got hit with this. Their POS system started processing returns for people who never bought anything, all because the timestamps were off by hours. The scammers used the gap to make fake returns look legit. That’s not a joke — they lost $120k before they fixed their time server setup.
Another big one: NTP amplification attacks. Wait, what’s that? So NTP servers can be tricked into sending way more data to a fake IP address than they receive. That’s a DDoS (distributed denial-of-service) attack in a nutshell. Bad actors spoof your target’s IP, send a tiny NTP request, and the server blasts a huge response at your network. We saw a healthcare client a while back get taken down for 36 hours because of this. Their EHR system was offline, which meant doctors couldn’t pull patient records. That’s the kind of risk that’s not just financial — it’s life-threatening for some industries.
Then there’s the stuff we call “outdated server firmware” or misconfigured settings. A lot of small businesses buy a cheap time server, set it up, and ignore it forever. They don’t update the OS, don’t enable encryption, leave default passwords (like admin/admin) on, and don’t restrict who can connect to the server. Last year, a small accounting firm we worked with had their time server compromised because they never changed the default login. The attackers got in, changed the time stamps on their tax files, making it look like they filed months early — and when the IRS audited them, they got hit with a huge penalty. The worst part? They had no idea their time server was even a weak point until we walked through their network.
Wait, and let’s not forget about open NTP servers. A lot of people leave their time servers open to anyone on the internet, thinking “it’s just time.” No, that’s a free pass for bad actors to use your server for those DDoS attacks we talked about. If your time server is open, you could be unknowingly helping someone take down a nearby business or even a whole city’s network. That’s a liability you don’t need.
But hold on — before you start panicking and ditch the time server altogether, let’s make something clear: these risks aren’t unavoidable. They only happen if you’re using a bad setup, a sketchy server, or not configuring it right. We’ve been in this game for years, and 9 out of 10 clients who hit issues were using cheap, unmanaged servers that didn’t have basic security features.
Let’s talk about what actually fixes these problems. First, use authenticated NTP. That means instead of sending time in plain text, your server uses keys to prove it’s the real deal, so devices know they’re not getting fake time. We build all our time servers with NTPv4 auth and even newer stuff like PTP (Precision Time Protocol) for super precise sync — perfect for data centers, finance firms, or anyone needing microsecond accuracy.
Second, keep your server updated. We push firmware updates every 90 days minimum, and we make it super easy to install ’em — no long, complicated processes that take your network offline. A lot of cheap server makers skip updates to save money, which leaves all those security gaps open. We don’t do that.
Third, lock down access. Don’t let just anyone connect to your time server. We let you set up IP whitelists, so only devices on your network can sync with it. No random internet users, no attackers from across the world messing with your time. We also disable default accounts by default — you have to make your own, unique login when you set it up. Simple stuff that makes a huge difference.
And here’s a key point: most people think “my network is small, so these risks don’t apply.” News flash: even a 10-person startup can get hit. We had a client in Seattle that ran a small marketing agency, and a bad actor used their open time server to launch a small DDoS attack on a client of theirs. The agency got sued because they didn’t secure their server — even though they didn’t mean to cause harm. That’s the kind of hidden risk no one warns you about.
Wait, let’s also mention the difference between public time servers and private ones. A lot of people use free public NTP servers from Google or Apple, and call it a day. But think about that: you’re sending your network’s time sync request to a third party server, over the internet. What if that server gets hacked? What if the provider has gaps in their security? We always recommend private time servers for businesses, because you control the whole thing — from the hardware to the software to who can access it. No relying on someone else’s uptime or security.
Let’s circle back to that retail client I mentioned earlier. After their incident, they switched to our time servers. We set them up with authenticated NTP, IP whitelisting, and regular firmware checks. Last month, they got a random NTP request that looked like a MITM attempt — our server blocked it automatically. They even sent us a note saying that without that, they probably would’ve lost another $50k. That’s the value of not cutting corners on this stuff.
So let’s get real for a second. The worst mistake you can make is treating your time server like an afterthought. It’s not a “set it and forget it” device. It’s one of the foundational parts of your network. If your time is off, everything else breaks — security, operations, customer trust.
Here’s what you should do right now, even if you’re not looking to switch servers: Grab someone from your IT team, log into your time server (or whatever device is syncing time), and check these four things: 1) Is auth enabled for NTP? 2) Are default passwords changed? 3) Are you only allowing trusted IPs to connect? 4) When was the last firmware update? If any of those are no answers, you’ve got a risk.
For us, this isn’t just selling a box. It’s making sure your business doesn’t get blindsided by something as silly as a wrong time stamp. We’ve helped hundreds of clients across industries — retail, healthcare, finance, startups — lock down their time servers so they don’t have to worry about these risks.
If you’re tired of dealing with sketchy time servers that leave gaps in your network, or you want to make sure your current setup is actually secure, hit us up to chat. We’ll walk through your specific setup, point out any risks, and show you how we can help. No sales pitch, no pressure — just real advice from people who’ve seen this stuff firsthand.
Don’t wait until you’re dealing with a breach, a lawsuit, or a business shutdown. Your time server matters.
Time and Frequency Synchronization References:
- Internet Engineering Task Force (IETF). Network Time Protocol Version 4: Protocol and Algorithms Specification. RFC 5905, 2010.
- US Computer Emergency Readiness Team (US-CERT). Security Implications of Network Time Protocol Usage. Technical Report, 2021.
- Global Cyber Alliance. Time Server Vulnerabilities and Mitigation Strategies. 2022.
- National Institute of Standards and Technology (NIST). Precision Time Protocol (PTP) for Networked Systems. Special Publication 800-181, 2020.
China Go-Sat Microwave Co., Ltd.
China Go-Sat Microwave Co., Ltd. is one of the most professional time sever manufacturers and suppliers in China. With abundant experience, we warmly welcome you to buy advanced time sever made in China here and get quotation from our factory. All customized products are with high quality and competitive price.
Address: No. 3908 ShiBo Avenue, Baqiao District, Xi’an, China
E-mail: sales@go-satcom.com
WebSite: https://www.go-satcom.com/
